Vulnerability Management
How the IvorySQL community handles security vulnerabilities - from reporting to disclosure.
Vulnerability Response
The IvorySQL community places a high priority on the security of its community edition. The IvorySQL Security Special Interest Group (SIG Security) is responsible for receiving, investigating, and disclosing security vulnerabilities related to the IvorySQL community. We encourage vulnerability researchers and industry organizations to proactively report suspected security vulnerabilities in IvorySQL to the SIG Security team. We aim to respond promptly, analyze, and resolve reported security issues or vulnerabilities.
As IvorySQL is based on PostgreSQL, vulnerabilities discovered and fixed in PostgreSQL also apply to IvorySQL. Our development team continuously monitors PostgreSQL community security information and promptly integrates PostgreSQL vulnerability patches into IvorySQL.
Supported Versions
The vulnerability response process primarily supports the latest release of the IvorySQL community edition and its branch versions.
Vulnerability Handling Process
Each security vulnerability is assigned a designated person for tracking and handling. This coordinator, a member of the IvorySQL SIG Security team, is responsible for overseeing the vulnerability remediation and disclosure. The end-to-end vulnerability handling process is outlined in the diagram below.
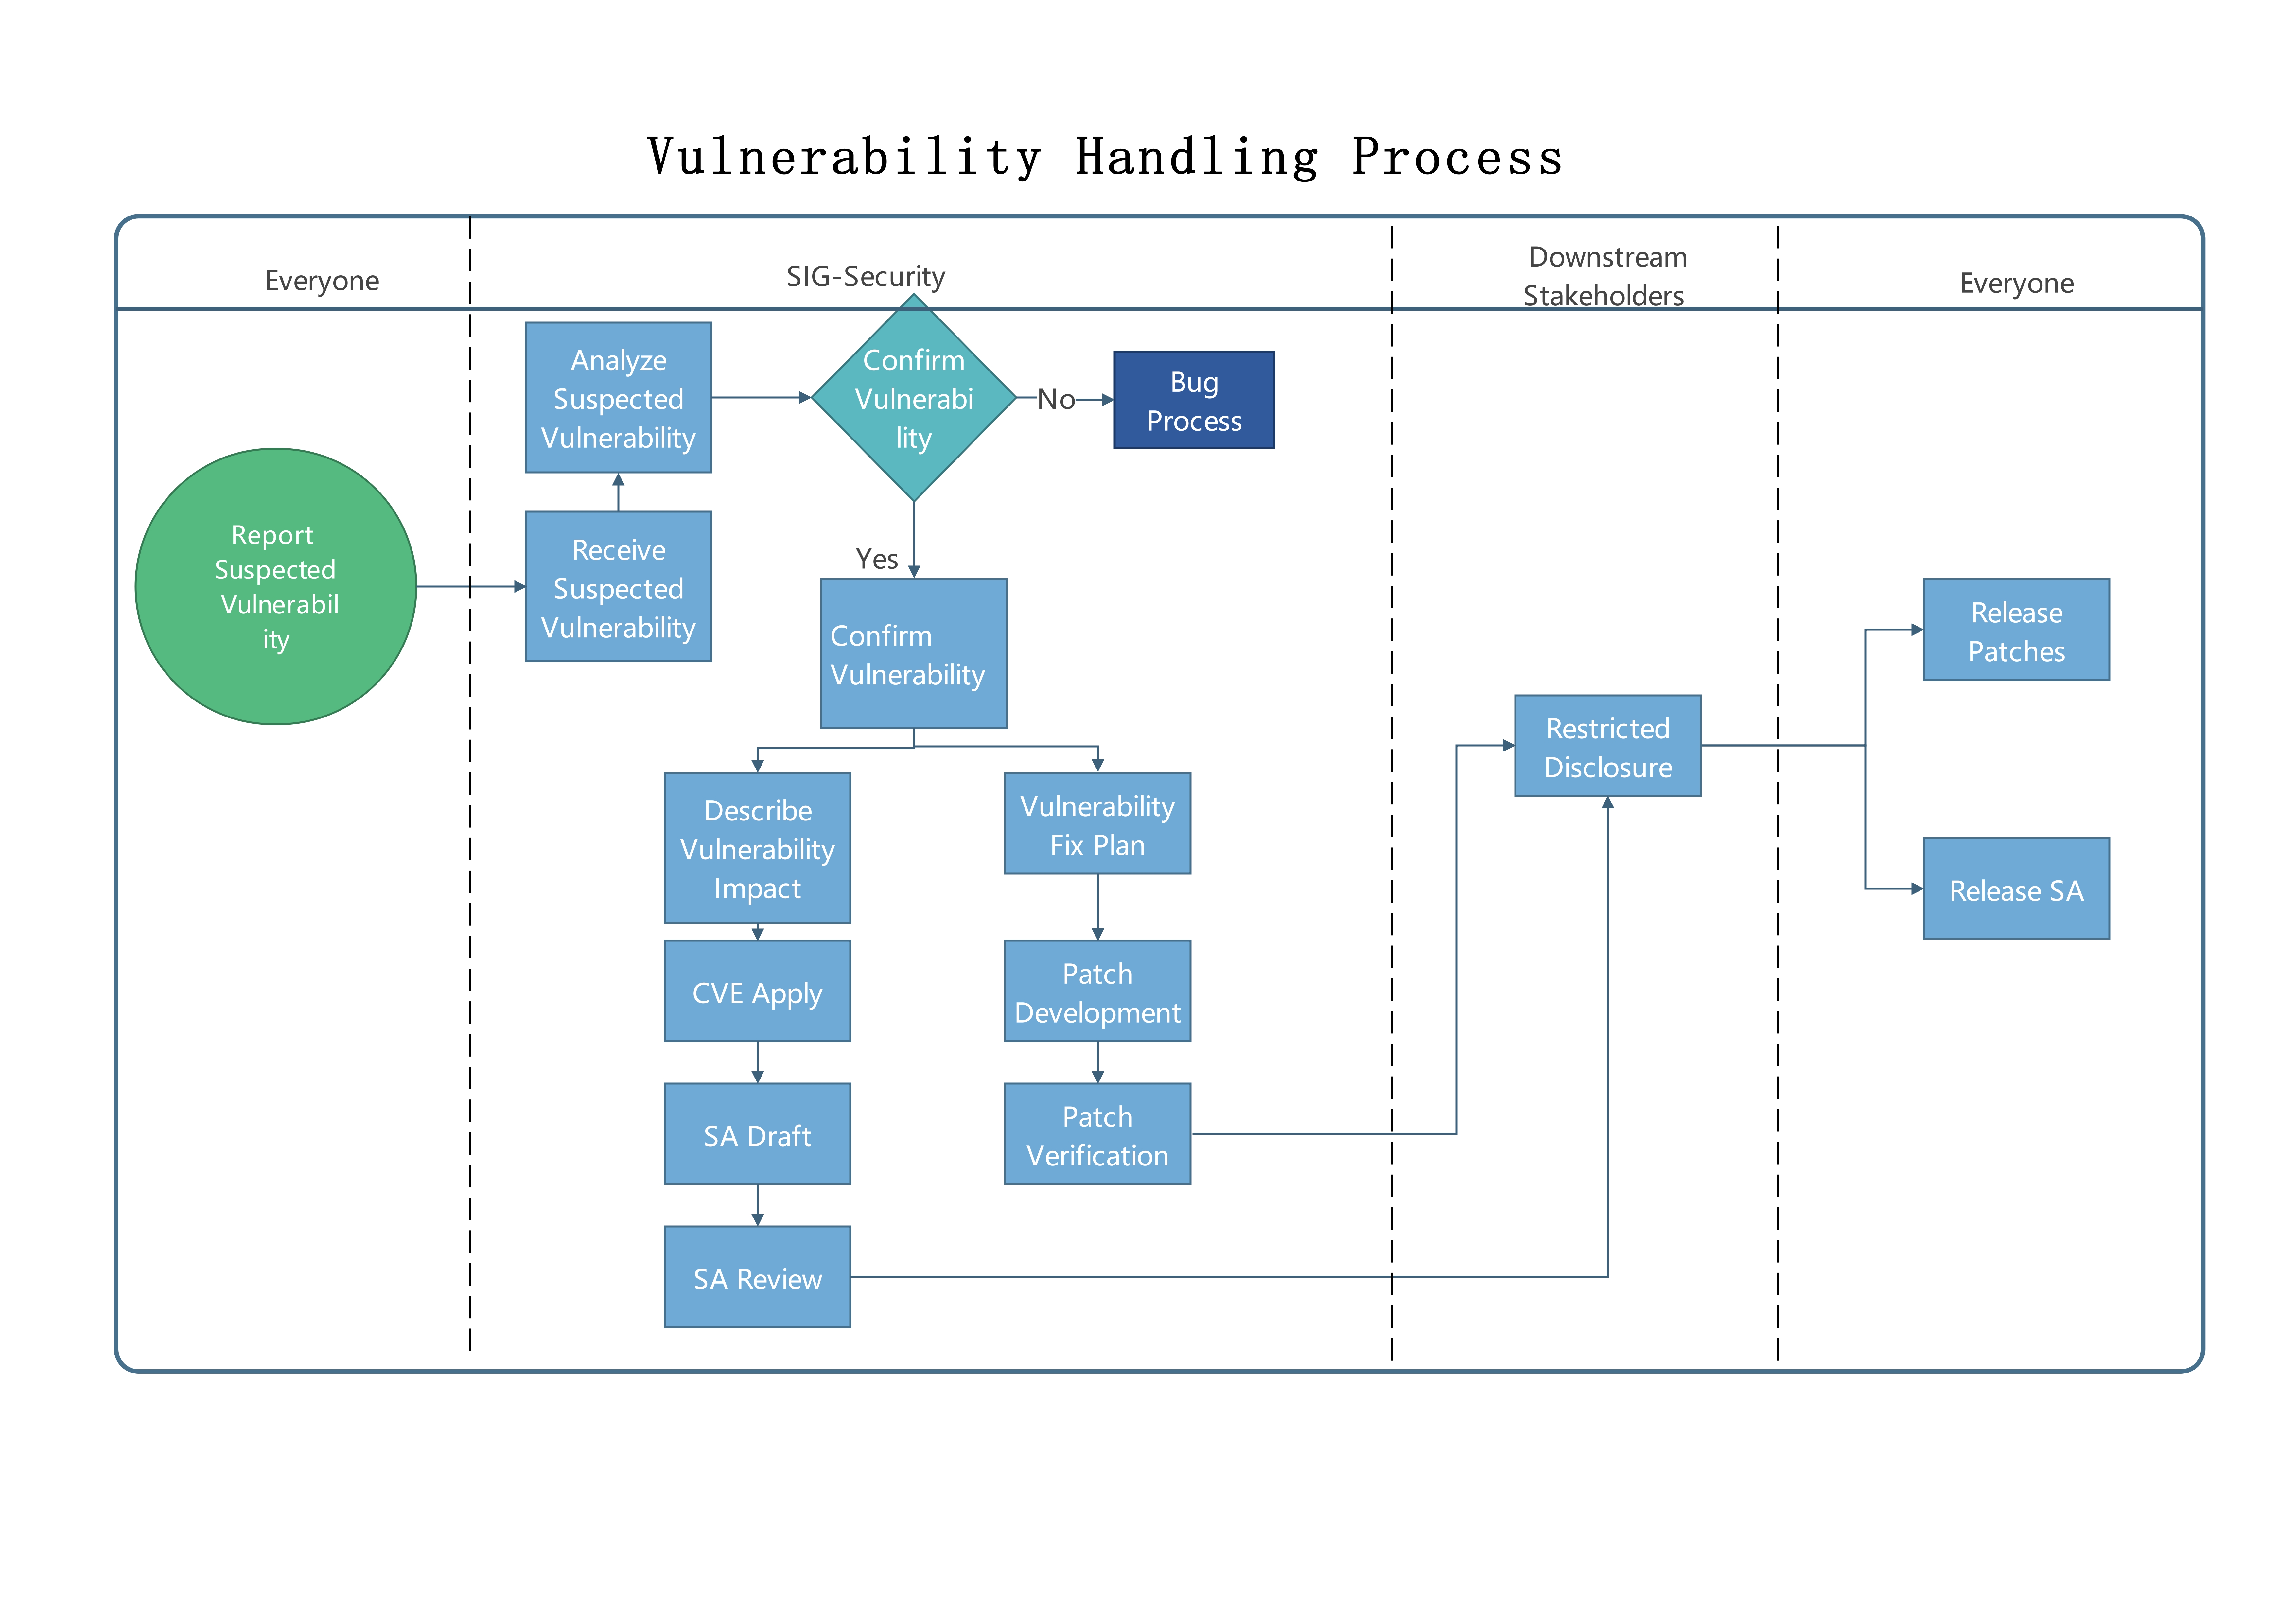
In this document, we focus on three key aspects of the process: vulnerability reporting, vulnerability assessment, and vulnerability disclosure.
Vulnerability Reporting
You can report potential security vulnerabilities in IvorySQL products by emailing the IvorySQL SIG Security team.
Required Information for Reporting
To facilitate rapid confirmation and verification of suspected vulnerabilities, please include the following information in your vulnerability report email:
Basic Information
Affected module, conditions triggering the vulnerability, and impact if successfully exploited.
Technical Details
System configuration, identification methods, exploit description, PoC, and steps to reproduce.
Suggested Remediation
Recommendations for fixing the vulnerability.
Reporter's Details
Organization and contact information of the reporter.
Disclosure Plan
Any planned disclosure timeline or intentions by the reporter.
Email Response Time
We will respond to suspected security vulnerabilities reported via email within 5 days and provide feedback on the progress of vulnerability handling to the reporter.
Vulnerability Severity Assessment
We assess vulnerability severity using the Common Vulnerability Scoring System (CVSS) standard:
Vulnerability Disclosure
To protect IvorySQL users, the community strictly limits vulnerability information during investigation and remediation. Information is shared only with personnel directly involved in handling the vulnerability. We do not publicly disclose, discuss, or confirm security issues until a fix is released. Once fixed, an announcement will be published via the securityannounce@ivorysql.org mailing list.